
HELM AI Kernel
Mindburn-Labs/helm-ai-kernel
Firewall fail-closed com isolamento de ferramentas e auditoria assinada para agentes IA
Ver no GitHubFirewall de execução fail-closed para agentes de IA que quarentena ferramentas MCP, faz proxy de requisições OpenAI-compatíveis, emite recibos assinados e verifica EvidencePacks offline. Fornece controle de segurança rigoroso para ambientes de agentes autônomos com assinatura criptográfica de operações.
Instalação
npx convez-ai Mindburn-Labs/helm-ai-kernel1 comando no terminal: detecta o formato do repositório (marketplace ou plugin avulso) e instala via Claude Code. Requer Node 18+ e o Claude Code instalado.
Métricas
Casos de uso
- Executar agentes IA com controle rigoroso de segurança em ambientes de produção
- Quarentena e proxy de chamadas MCP para validação antes de execução
- Auditoria criptográfica e verificação offline de operações de agentes
Veredito

Solução enterprise-grade para governança de agentes IA com arquitetura fail-closed, assinatura criptográfica e verificação offline. Altamente recomendado para deployments críticos que exigem auditoria e controle granular.
README
A tradução para o português deste README ainda está na fila.
HELM AI Kernel


HELM AI Kernel is the fail-closed execution firewall for AI agents.
Mindburn Labs' HELM execution kernel for AI agents, not the Kubernetes package manager.
HELM evaluates agent execution requests and records every ALLOW / DENY / ESCALATE decision as verifiable evidence.
Try HELM AI Kernel Locally
No account, hosted service, or production credential is required for the local proof path:
git clone https://github.com/Mindburn-Labs/helm-ai-kernel.git
cd helm-ai-kernel
make build
bash scripts/launch/demo-mcp.sh
bash scripts/launch/demo-proof.sh
The local proof path shows the public value proposition in one frame:
- unknown MCP servers and tools are denied before fixture dispatch
- a schema-pinned fixture call is allowed
- a signed DENY receipt verifies offline
- a flipped-verdict receipt fails verification
Star HELM AI Kernel if you want to follow fail-closed AI agent execution, MCP quarantine, signed receipts, and offline-verifiable EvidencePacks: https://github.com/Mindburn-Labs/helm-ai-kernel/stargazers
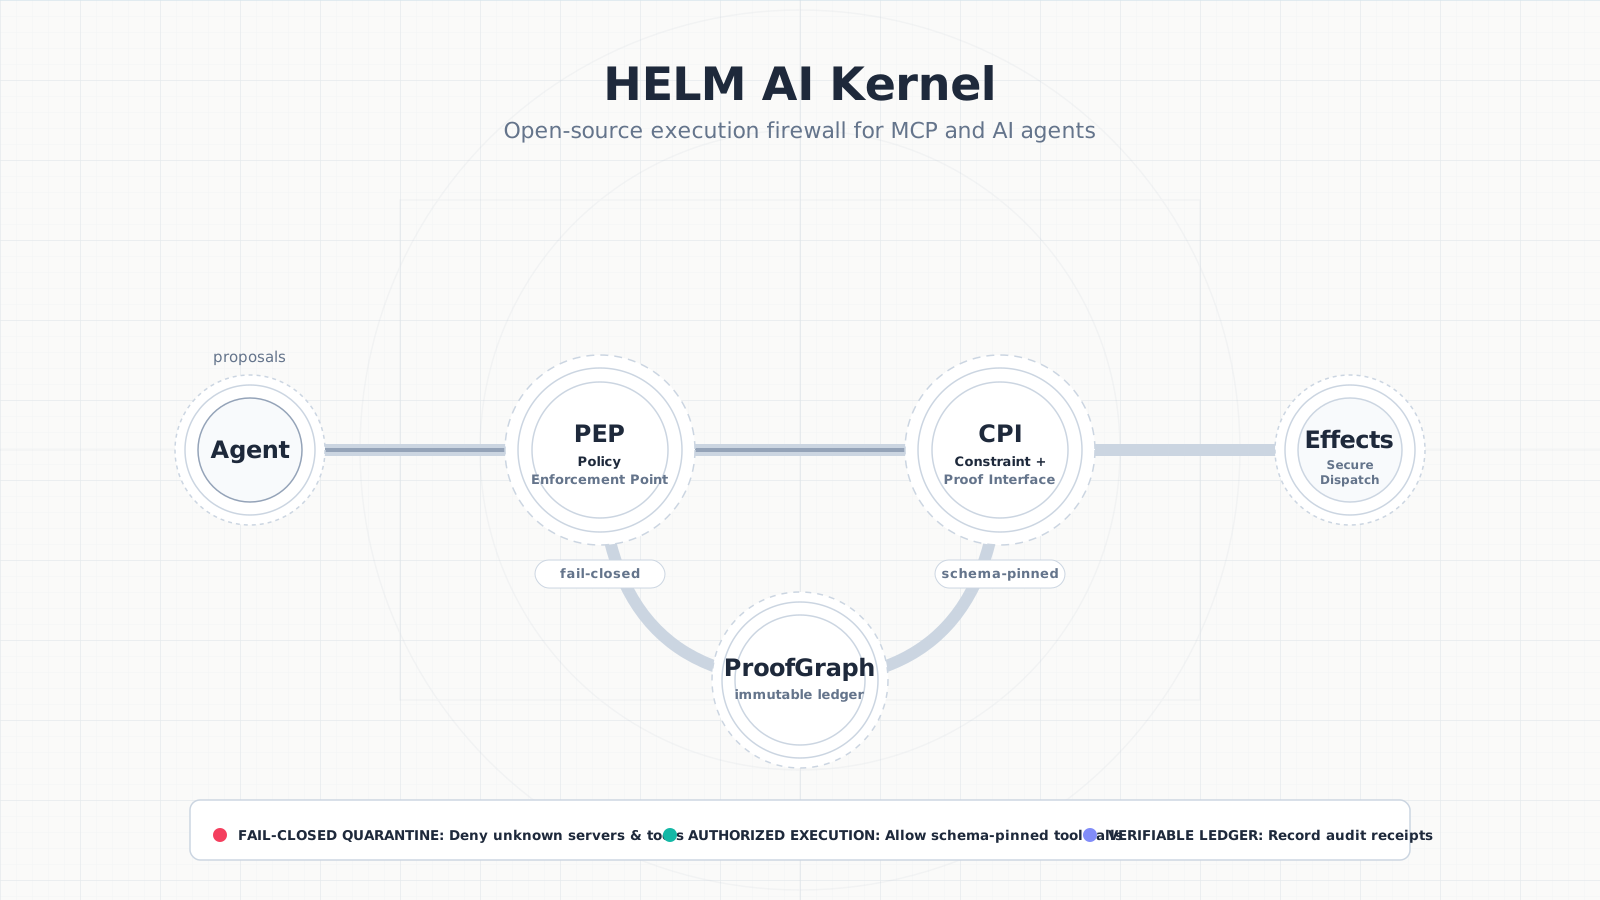
Sanitized transcripts are checked in under
examples/launch/assets.
Start Here
| Visitor | First path | What to verify |
|---|---|---|
| Agent builders | Quickstart and OpenAI-compatible proxy | Existing OpenAI-style clients can route through HELM and receive receipt metadata. |
| Security engineers | Execution Security Model and OWASP MCP Threat Mapping | ALLOW, DENY, and ESCALATE decisions are recorded with verifiable evidence. |
| Gateway and MCP maintainers | MCP integration and Ecosystem map | Unknown tools stay quarantined until schema, identity, and policy state are approved. |
Community And Product Links
- Try HELM AI Kernel locally: Quickstart
- Star on GitHub: Mindburn-Labs/helm-ai-kernel
- Join Discussions: GitHub Discussions
- Find first issues: good first issue
- Talk to Mindburn Labs about production execution authority: Console
Launchpad And Console
brew install mindburnlabs/tap/helm-ai-kernel
helm-ai-kernel login
helm-ai-kernel console pair

export OPENROUTER_API_KEY=...
helm-ai-kernel launch secrets set model_gateway \
  --provider openrouter \
  --value-env OPENROUTER_API_KEY

helm up openclaw
helm up hermes --target local

helm-ai-kernel launch evidence <launch_id> --export --json
helm-ai-kernel verify --bundle <pack>
Native EvidencePack verification is sealed by
07_ATTESTATIONS/evidence_pack.sig. Dev-local packs verify offline with the
default profile. Customer-grade packs use the same seal plus explicit trust
configuration, external signing, an external Rekor or RFC3161 anchor receipt,
and an S3 Object Lock storage receipt:
helm-ai-kernel trust init --config helm/helm.yaml --profile customer --signer kms --anchor rekor --store s3 --object-lock
helm-ai-kernel verify --bundle <pack.tar> --profile customer --storage-receipt <pack.tar.storage.json>
What you get:
- Console dashboard with receipts, evidence, and run history
- deterministic ALLOW / DENY / ESCALATE verdicts
- MCP quarantine for unknown servers and tools
- signed receipts
- offline-verifiable EvidencePacks
- teardown proof
Core Overview
AI models propose. Deterministic systems govern. HELM sits between stochastic agent tool calls and infrastructure side effects. It intercepts MCP tools and OpenAI-compatible requests, evaluates authority before dispatch, and emits signed receipts that can be verified offline.
This is Mindburn Labs' HELM execution kernel for AI, not the Kubernetes package manager.
Agent proposal -> HELM boundary -> ALLOW / DENY / ESCALATE -> signed receipt
Status
- Repository:
Mindburn-Labs/helm-ai-kernel - Root package identity:
helm-ai-kernel-root - Source release target:
v0.5.10 - License: Apache-2.0
- Supported security line:
0.5.x;0.4.xis best effort - Canonical docs: https://helm.docs.mindburn.org/helm-ai-kernel
The v0.5.10 release is complete only when the GitHub Release includes
CLI binaries, checksums, SBOM JSON, OpenVEX, release-attestation metadata,
Cosign bundles, evidence-pack.tar, helm-ai-kernel.mcpb,
helm-ai-kernel.rb, sample policy material, and a passing
version-status.json for all lockstep package channels:
https://github.com/Mindburn-Labs/helm-ai-kernel/releases/tag/v0.5.10.
What HELM AI Kernel Does
- Enforces default-deny execution for agent tool calls.
- Wraps MCP servers so unknown tools can be quarantined before side effects.
- Runs the kernel, guardian, proxy, receipt store, evidence export, and verification paths.
- Produces signed receipts and EvidencePacks for replay, audit, and tamper checks.
- Ships public SDK sources for Go, Python, TypeScript, Rust, and Java.
HELM AI Kernel does not include hosted Mindburn operations, private operational tooling, or non-OSS downstream extensions.
Quick Start
Register at https://console.helm.mindburn.org to create your account, then
install the published macOS CLI from the current GitHub release. The public
Homebrew tap is current only when the release includes a passing
version-status.json.
curl -L -o helm-ai-kernel https://github.com/Mindburn-Labs/helm-ai-kernel/releases/latest/download/helm-ai-kernel-darwin-arm64
chmod +x helm-ai-kernel
./helm-ai-kernel --version
Start a local headless boundary:
helm-ai-kernel serve --policy ./release.high_risk.v3.toml
helm-ai-kernel boundary status
Run the local proof demo after helm-ai-kernel serve starts on 127.0.0.1:7714:
curl http://127.0.0.1:7714/api/demo/run \
  -H 'content-type: application/json' \
  -d '{"action_id":"export_customer_list","policy_id":"agent_tool_call_boundary"}'
Verify the returned receipt and confirm that tampering fails:
curl http://127.0.0.1:7714/api/demo/verify \
  -H 'content-type: application/json' \
  -d '{"receipt":{...},"expected_receipt_hash":"<receipt_hash from proof_refs>"}'

curl http://127.0.0.1:7714/api/demo/tamper \
  -H 'content-type: application/json' \
  -d '{"receipt":{...},"expected_receipt_hash":"<receipt_hash from proof_refs>","mutation":"flip_verdict"}'
Govern MCP tools or an OpenAI-compatible client:
python3 scripts/launch/mock-openai-upstream.py --port 19090
helm-ai-kernel mcp wrap --server-id local-tools --upstream-command "python3 scripts/launch/mcp-fixture-server.py"
helm-ai-kernel proxy --upstream http://127.0.0.1:19090/v1
Inspect and verify evidence:
helm-ai-kernel sandbox preflight --runtime wazero
helm-ai-kernel receipts tail --agent agent.demo.exec
helm-ai-kernel verify evidence-pack.tar
helm-ai-kernel serve --policy stores receipts in SQLite by default unless
DATABASE_URL is set. helm-ai-kernel verify evidence-pack.tar runs offline by default;
use --online only when public proof endpoint credentials are available for
that release.
Build From Source
git clone https://github.com/Mindburn-Labs/helm-ai-kernel.git
cd helm-ai-kernel
make build
./bin/helm-ai-kernel serve --policy ./release.high_risk.v3.toml
Run the retained validation targets before publishing changes:
make test
make test-platform
make test-all
make crucible
Architecture
HELM separates orchestration from execution authority. Agent frameworks decide what to attempt; HELM decides what is allowed to execute.
flowchart LR
    Agent["Agent tool call"] --> Boundary["HELM boundary"]
    Boundary --> Verdict["ALLOW / DENY / ESCALATE"]
    Verdict --> Receipt["Signed receipt"]
    Receipt --> Verify["Verify / replay"]
    Verify --> Tamper["Tamper fails"]
Unknown MCP servers and tools enter quarantine before dispatch:
flowchart TD
    Server["Discovered MCP server"] --> Quarantine["Quarantined by default"]
    Quarantine --> Inspect["Metadata and schema inspection"]
    Inspect --> Risk["Risk classification"]
    Risk --> Approval["Approval record"]
    Approval --> Active["Policy-bound active state"]
    Active --> Decision["ALLOW / DENY / ESCALATE"]
    Decision --> Proof["Receipt and ProofGraph event"]
Key terms:
ALLOW: HELM lets the action run.DENY: HELM blocks the action.ESCALATE: HELM stops and asks for more facts, policy, or human approval.Receipt: signed record of the decision.ProofGraph: replayable record chain for what happened.EvidencePack: portable bundle of records for a review path.
The complete diagram doctrine lives in docs/architecture/canonical-diagrams.md.
Public Interfaces
| Surface | Path | Status |
|---|---|---|
| CLI and kernel | core/ | Go implementation of boundary, CLI, HTTP API, proxy, receipts, evidence export, and verification |
| Headless API contract | api/openapi/, protocols/, schemas/ | HTTP, WebSocket-adjacent, OpenAPI, Protobuf, policy schema, and JSON schema contracts for external clients |
| Wire contracts | api/openapi/, protocols/, schemas/ | OpenAPI, Protobuf, policy schemas, and JSON schemas |
| SDKs | sdk/ | Go, Python, TypeScript, Rust, and Java sources |
| Examples | examples/ | Runnable integrations and launch smoke material |
| Conformance | tests/conformance/, reference_packs/ | Profile, checklist, fixtures, and reference packs |
| Deployment | deploy/helm-chart/ | Helm chart for running the kernel in Kubernetes |
SDKs And Packages
| Surface | Current install or status |
|---|---|
| CLI | GitHub Release binaries; the latest release attaches a helm-ai-kernel.rb formula asset. Verify the public tap before relying on brew install mindburnlabs/tap/helm-ai-kernel for the latest version |
| Go SDK | go get github.com/Mindburn-Labs/helm-ai-kernel/sdk/go@main; tagged module versions are tracked as an OSS-readiness follow-up |
| Python SDK | pip install helm-sdk |
| TypeScript SDK | npm install @mindburn/helm-ai-kernel |
| Rust SDK | cargo add helm-sdk |
| Java SDK | Maven Central coordinate io.github.mindburnlabs:helm-sdk:0.5.10 |
HTTP clients are generated from
api/openapi/helm.openapi.yaml. Protobuf
message bindings come from protocols/proto/ where a
language SDK ships them.
Documentation
Public OSS docs are sourced from this repo and published through
helm.docs.mindburn.org. The owned docs set for sync is declared in
docs/public-docs.manifest.json.
- Quickstart
- Community
- Ecosystem
- HELM AI Kernel OSS Traction Plan
- Architecture
- Conformance
- Verification
- Publishing
- Compatibility
- SDK Index
- Security Model
- OWASP Mapping
- NIST AI Agent Critical Infrastructure Alignment
- NIST AI RMF to ISO 42001 Crosswalk
- Search-intent pages: MCP tool quarantine, AI agent execution firewall, OpenAI-compatible execution boundary, signed receipts for AI agent actions, and AI agent side-effect governance
Release Verification
For v0.5.10, verify downloads with SHA256SUMS.txt, sbom.json,
v0.5.10.openvex.json, release-attestation.json, the platform binary assets,
matching *.cosign.bundle files, and offline evidence-pack.tar verification.
Current release tooling requires tag refs to match the checked-in VERSION,
requires an exact v<version>.openvex.json for tag releases, and verifies the
staged evidence-pack.tar before checksums are finalized.
See docs/VERIFICATION.md and docs/PUBLISHING.md for the full release verification path.
Security, Contributing, And Governance
- Report vulnerabilities through SECURITY.md. Do not open public issues for security-sensitive reports.
- Contribution setup and validation expectations are in CONTRIBUTING.md.
- Project governance and maintainer responsibilities are in GOVERNANCE.md and MAINTAINERS.md.
- Community behavior expectations are in CODE_OF_CONDUCT.md.
- Support channels are listed in SUPPORT.md.
- Near-term OSS work is summarized in ROADMAP.md.
License
Apache-2.0. See LICENSE.